Nmap (Network Mapper) is a free, open-source tool for network discovery, port scanning, and security auditing. This nmap cheat sheet covers every command, flag, and scan type you need, from basic host discovery to advanced firewall evasion.
Use it as a quick reference during penetration tests, network audits, or CTF challenges.
TL;DR
- Nmap scans networks to find live hosts, open ports, running services, and operating systems.
- The most common command is nmap -sV -sC -O -p- <target> for a full service and OS scan.
- SYN scan (-sS) is the default and fastest scan type for most users with root/admin privileges.
- NSE scripts (-sC or –script) extend Nmap with vulnerability checks, brute-forcing, and enumeration.
- Always get written authorization before scanning any system you don’t own.
Most Useful Nmap Commands (90% real-world scanning)
| Task | Command |
|---|---|
| Quick default scan | nmap <target> |
| Ping sweep (host discovery) | nmap -sn 192.168.1.0/24 |
| Stealth SYN scan | nmap -sS <target> |
| TCP connect scan (no root) | nmap -sT <target> |
| Scan specific ports | nmap -p 22,80,443 <target> |
| Scan all 65,535 ports | nmap -p- <target> |
| Fast scan (top 100 ports) | nmap -F <target> |
| Detect service versions | nmap -sV <target> |
| Detect operating system | nmap -O <target> |
| Run default NSE scripts | nmap -sC <target> |
| Aggressive all-in-one scan | nmap -A <target> |
| Faster timing template | nmap -T4 <target> |
| IPv6 scan | nmap -6 <target> |
| Save output in all formats | nmap -oA results <target> |
Before running any of the commands in this cheat sheet, it is strongly recommended to practice in a controlled environment. Here’s a complete guide on how to set up a penetration testing lab so you can safely test Nmap techniques.
What Is Nmap?
Nmap is a command-line tool that discovers devices on a network and identifies the services those devices are running. Security teams use it for vulnerability assessments, network inventory, and penetration testing.
It works by sending crafted packets to target hosts and analyzing the responses it gets back.
Core capabilities:
- Host discovery: find live devices on a network
- Port scanning: find open, closed, and filtered ports
- Service and version detection
- Operating system fingerprinting
- Scriptable interaction via the Nmap Scripting Engine (NSE)
Target Specification
Nmap accepts single IPs, ranges, subnets, hostnames, and target list files as scan targets.
| Syntax | Example | Description |
|---|---|---|
| Single IP | nmap 192.168.1.10 | One host |
| Hostname | nmap example.com | Resolves DNS first |
| IP range | nmap 192.168.1.1-50 | Range of last octet |
| CIDR block | nmap 192.168.1.0/24 | Entire subnet |
| Multiple targets | nmap 192.168.1.1 192.168.1.5 | Space-separated |
| Target list from file | nmap -iL targets.txt | One target per line |
| Exclude hosts | nmap 192.168.1.0/24 –exclude 192.168.1.1 | Skip specific hosts |
| Random targets | nmap -iR 10 | Scan 10 random public IPs (use with caution) |
Host Discovery
Host discovery finds which devices are online before Nmap scans any ports, which saves time on large networks.
| Flag | Purpose | When to Use |
|---|---|---|
| -sn | Ping scan only, no port scan | Fast inventory of live hosts |
| -Pn | Skip host discovery, treat all as up | Target blocks ping/ICMP |
| -PS<ports> | TCP SYN discovery | Bypassing ICMP-blocking firewalls |
| -PA<ports> | TCP ACK discovery | Evading stateless firewalls |
| -PU<ports> | UDP discovery | Detecting UDP-only hosts |
| -PE | ICMP echo discovery | Standard internal network ping |
| -n | Disable DNS resolution | Speed up large scans |
| -R | Force DNS resolution | Confirm hostnames |
Example — find all live hosts on a /24 subnet without touching any ports:
nmap -sn 10.0.0.0/24Scan Types (With When-to-Use Notes)
A scan type tells Nmap which kind of packet to send to determine whether a port is open, closed, or filtered. The mechanics of each technique are documented in the official Port Scanning Techniques guide.
| Flag | Scan Type | When to Use |
|---|---|---|
| -sS | TCP SYN scan | Default choice — fast, stealthy, requires root |
| -sT | TCP Connect scan | No root access available |
| -sU | UDP scan | Checking DNS, SNMP, DHCP services |
| -sA | ACK scan | Mapping firewall rule sets |
| -sW | Window scan | Advanced firewall analysis |
| -sN | Null scan | Firewall/IDS evasion testing |
| -sF | FIN scan | Stealth evasion against older firewalls |
| -sX | Xmas scan | Evasion, unusual flag combination |
| -sO | IP protocol scan | Identify supported protocols (TCP, UDP, ICMP) |
| -sY | SCTP INIT scan | Testing SCTP-based services (telecom) |
Practical rule: Use -sS for most scans. Reach for -sU only when UDP services matter, and use Null/FIN/Xmas scans only in controlled evasion testing.
Port Specification
Port specification flags control exactly which ports Nmap checks, which directly affects scan speed and accuracy. See the official Port Specification and Scan Order guide for advanced syntax.
| Command | Result |
|---|---|
| -p 80 | Scan port 80 only |
| -p 22,80,443 | Scan specific ports |
| -p 1-1000 | Scan a port range |
| -p- | Scan all 65,535 ports |
| -p U:53,T:80 | Mix UDP and TCP ports |
| -F | Fast scan — top 100 ports |
| –top-ports 20 | Scan the 20 most common ports |
| -r | Scan ports sequentially, not randomized |
Service & OS Detection
Service and OS detection identify the exact software version and operating system running on a target, which is essential for finding known vulnerabilities. Nmap’s official docs cover Service and Version Detection and OS Detection in full depth.
| Flag | Purpose |
|---|---|
| -sV | Detect service/version on open ports |
| –version-intensity 9 | Maximum detection accuracy (slower) |
| -O | Detect operating system |
| –osscan-guess | Guess OS aggressively when uncertain |
| -A | Combines -sV, -O, -sC, and traceroute |
Example — reveal both service banners and likely OS in one pass:
nmap -sV -O 192.168.1.1
Timing & Performance
Timing templates control how fast Nmap scans, trading speed against stealth, higher numbers scan faster but are easier for firewalls and IDS systems to detect. The official Timing and Performance guide covers every tunable option.
| Template | Flag | Use Case |
|---|---|---|
| Paranoid | -T0 | Maximum stealth, IDS evasion |
| Sneaky | -T1 | Slow, low-detection scans |
| Polite | -T2 | Reduces bandwidth/target load |
| Normal | -T3 | Default speed |
| Aggressive | -T4 | Fast, recommended for most pentests |
| Insane | -T5 | Fastest, high chance of inaccurate results |
Other performance flags:
- –min-rate 1000 — sends packets no slower than 1000/sec
- –max-retries 2 — limits retransmissions on unresponsive ports
- –host-timeout 30m — skips slow/unresponsive hosts after 30 minutes
Output Formats
Nmap can save scan results as plain text, XML, or grepable output, so results can be reused in reports or fed into other tools. Full format specs are in the official Output guide.
| Flag | Format | Use Case |
|---|---|---|
| -oN file.txt | Normal text | Human-readable report |
| -oX file.xml | XML | Import into other tools |
| -oG file.gnmap | Grepable | Scripting and parsing |
| -oA basename | All formats at once | Saves .nmap, .xml, .gnmap together |
| -v / -vv | Verbose / extra verbose | Live scan progress |
| -d | Debug output | Troubleshooting scan issues |
See also: Wireshark Cheat Sheet: Complete Filters, Shortcuts & Commands (2026)
NSE Scripts (Most Useful Ones)
The Nmap Scripting Engine (NSE) runs Lua scripts that automate vulnerability detection, enumeration, and brute-forcing directly during a scan. NSE scripts are grouped into categories — such as vuln, auth, brute, discovery, and safe — so you can target exactly the kind of check you need. Browse every available script in the official NSEDoc Reference Portal.
| Command | Purpose |
|---|---|
| -sC | Run default safe scripts |
| –script vuln | Check for known vulnerabilities |
| –script safe | Run only non-intrusive scripts |
| –script auth | Test for authentication bypass issues |
| –script brute | Attempt credential brute-forcing |
| –script discovery | Gather extra host/service info |
| –script http-title | Grab webpage titles |
| –script smb-os-discovery | Identify Windows OS via SMB |
| –script ftp-anon | Test for anonymous FTP login |
| –script ssl-heartbleed | Check for Heartbleed vulnerability |
| –script dns-brute | Brute-force subdomains via DNS |
| –script-args user=admin,pass=pass | Pass custom arguments to scripts |
| –script-updatedb | Update the NSE script database |
Scripts can be combined and scoped to a specific port for faster, targeted checks.
Example — check a single host for the Heartbleed bug:
nmap -p 443 --script ssl-heartbleed <target>Example — run multiple script categories at once:
nmap -sV --script "vuln,safe" -p 80,443 <target>Keep NSE current with nmap –script-updatedb since new vulnerability scripts are added as CVEs are disclosed — this matters most for 2026 engagements, where recently published scripts often cover the latest known flaws.
For a practical shortlist of the most useful scripts in real engagements, see this focused guide on the top 10 NSE scripts every penetration tester should know.
Firewall & IDS Evasion
Firewall and IDS evasion flags manipulate packet structure and timing to test whether security controls detect or block a scan. Use these only during authorized penetration tests to validate detection controls, never against systems without permission.
| Flag | Technique | When to Use |
|---|---|---|
| -f | Fragment packets | Bypass simple packet filters |
| -D RND:10 | Decoy scan with 10 random IPs | Obscure the real scanning source |
| -S <spoofed-IP> | Spoof source IP | Testing IP-based access controls |
| -g 53 | Use a specific source port (e.g., DNS) | Bypass port-based firewall rules |
| –data-length 25 | Append random data to packets | Avoid signature-based detection |
| –mtu 8 | Set custom packet size | Fragment evasion |
| -e eth0 | Specify network interface | Multi-homed systems |
Example — combine fragmentation with a decoy scan for evasion testing:
nmap -f -D RND:10 -sS <target>Recommended Scan Sequences for Real Engagements
A structured scan sequence from host discovery to vulnerability checks — produces faster, more accurate results than running one large scan at once. These steps build on the official Nmap Usage Examples.
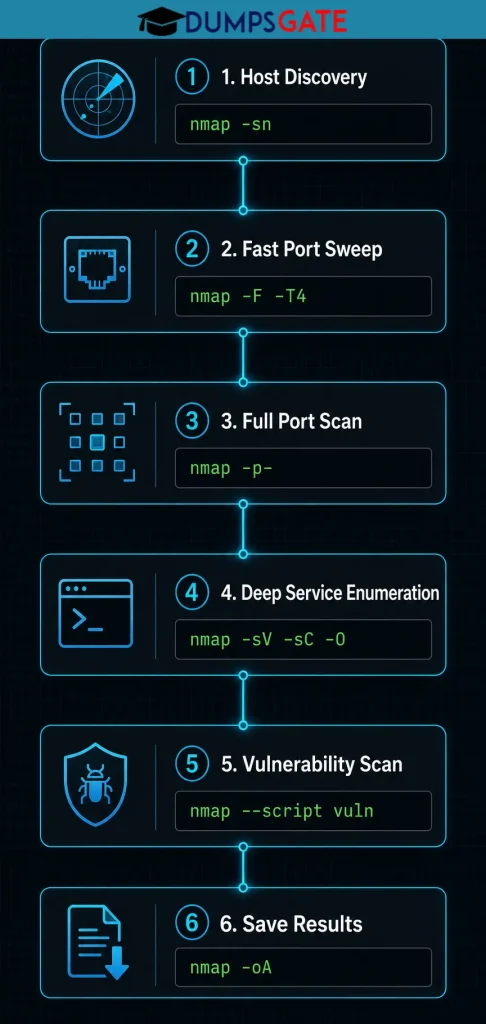
1. Initial Reconnaissance
nmap -sn 192.168.1.0/24Find all live hosts before deeper scanning.
2. Fast Port Sweep
nmap -F -T4 <target>Quickly identify common open ports.
3. Full Port Scan
nmap -p- -T4 <target>Confirm no ports were missed.
4. Deep Service Enumeration
nmap -sV -sC -O -p <open-ports> <target>Gather service versions, OS, and default script results on confirmed open ports.
5. Vulnerability Scan
nmap --script vuln -p <open-ports> <target>Check discovered services against known CVEs.
Once you have identified potential vulnerabilities with Nmap, the next logical step is exploitation. A detailed overview of the most widely used exploitation frameworks can help you move from discovery to controlled testing efficiently.
6. Report and Save
nmap -oA final_scan <target>Store results in all formats for the final report.
Modern Tips (IPv6, Cloud & Containers)
Modern Nmap usage increasingly involves IPv6 networks, cloud infrastructure, and containerized services, each with its own scanning considerations.
IPv6 scanning: Use -6 to scan IPv6 addresses; combine with -sS -6 for stealth SYN scans over IPv6:
nmap -6 -sS <IPv6-target>
- Cloud environments: Many cloud providers (AWS, Azure, GCP) block unsolicited scans by default and may flag or suspend accounts that trigger them — always confirm scanning is permitted under your provider’s acceptable use policy and, where required, file a scan-authorization request first.
- Containers: Scan container networks directly by targeting the container’s internal IP; –top-ports is useful for quickly checking exposed microservice ports without a full sweep.
- Kubernetes/orchestrated environments: Combine -sn with a CIDR scan of the pod network range to inventory live pods before targeted port scans, since IPs are often reassigned dynamically.
- Rate-limiting awareness: Cloud security groups and WAFs increasingly auto-block aggressive scans — use -T2 or -T3 and –max-retries in cloud contexts to avoid triggering lockouts.
- Script freshness: Run nmap –script-updatedb before major 2026 engagements so NSE checks reflect the most recently disclosed vulnerabilities.
- Version awareness: Always confirm you’re running a current Nmap release (nmap -V) since IPv6, NSE, and detection accuracy all improve with newer builds.
Download Free PDF – Nmap Cheat Sheet 2026 PDF
Frequently Asked Questions
What is Nmap used for?
Nmap is used to discover live hosts on a network, scan for open ports, identify running services, and detect operating systems for security auditing and network management.
Is Nmap legal to use?
Nmap is legal to use on networks and systems you own or have explicit written permission to test. Scanning systems without authorization is illegal in most countries.
What is the difference between -sS and -sT scans?
-sS (SYN scan) is faster and stealthier but requires root/administrator privileges. -sT (Connect scan) completes the full TCP handshake and works without elevated privileges.
How do I scan all ports with Nmap?
Run nmap -p- <target> to scan all 65,535 TCP ports on a target.
What does the -A flag do in Nmap?
The -A flag enables OS detection, version detection, script scanning, and traceroute in a single command.
How do I make Nmap scans faster?
Use a higher timing template (-T4), limit the port range with -p, and increase the packet rate with –min-rate.
What is NSE in Nmap?
NSE (Nmap Scripting Engine) is a framework that runs Lua scripts to automate tasks like vulnerability detection, brute-forcing, and service enumeration.
Can Nmap detect firewalls?
Yes. An ACK scan (-sA) helps map firewall rule sets by identifying which ports are filtered versus unfiltered.
How do I scan for a specific vulnerability with Nmap?
Run an NSE vulnerability script, for example nmap –script ssl-heartbleed -p 443 <target>, to check for a specific known flaw.
Does Nmap work on Windows, macOS, and Linux?
Yes. Nmap is cross-platform and available for Windows, macOS, and all major Linux distributions.
What is the fastest Nmap scan command?
nmap -F -T4 <target> scans the top 100 ports quickly using an aggressive timing template.
How do I save Nmap results to a file?
Use -oN file.txt for a text report, -oX file.xml for XML, or -oA basename to save all formats at once.
If you prefer a more permanent practice environment, this guide shows how to build a home penetration lab that you can use for ongoing Nmap practice and full engagement simulations.
Disclaimer
Nmap is a powerful network scanning tool that must only be used on systems and networks you own or have explicit, written authorization to test. Unauthorized scanning of networks, servers, or devices you do not control may violate laws such as the Computer Fraud and Abuse Act (U.S.), the Computer Misuse Act (U.K.), and equivalent legislation in other countries.
This article is provided for educational and authorized security testing purposes only. Dumpsgate is not responsible for misuse of the information contained in this cheat sheet.