ISO 27001 certification costs most small and mid-sized companies between $10,000 and $50,000 for the first year, with large or multi-location organizations often spending $75,000 to $200,000 or more. The certification audit itself, paid directly to an accredited certification body, typically runs $7,000 to $25,000 depending on company size.
That is the vendor-quoted range you will see almost everywhere. Below, you will also see what the number actually depends on, what people report paying in practice, and where you can genuinely spend less.
What Does ISO 27001 Certification Cost by Company Size?
Your headcount sets the audit fee. ISO/IEC 27006, the standard accredited certification bodies must follow, links recommended audit days to the number of employees in scope, and the certification body multiplies those days by its day rate (source: GRC Solutions, ISO 27001 cost guide).
Audit fee = audit days × the certification body’s day rate.
| Employees in scope (from) | Audit days, Stage 1 + Stage 2 | Audit fee at an assumed $1,500/day |
|---|---|---|
| 1 | 5 | $7,500 |
| 11 | 6 | $9,000 |
| 26 | 9 | $13,500 |
| 46 | 10 | $15,000 |
| 86 | 12 | $18,000 |
| 126 | 13 | $19,500 |
| 426 | 17 | $25,500 |
| 1,176 | 20 | $30,000 |
The $1,500 day rate is an assumption for illustration, so swap in the rate from each quote you receive. A certification body may cut audit time to as little as 70% of the recommendation, which is one reason quotes for the same company differ. Add preparation, consulting, and software from the next section to get your first-year total.
ISO 27001 Certification Cost Calculator
Estimate your audit fee and first-year budget in a few seconds.
| Certification audit (Stage 1 + Stage 2), … | … |
| Preparation | … |
| Internal audit and penetration testing | … |
Multiple locations add audit days beyond this estimate. Ask each certification body for a site-specific quote.
Audit days follow the ISO/IEC 27006 headcount guidance; a certification body may audit for as little as 70% of the recommended time, which sets the low end. Years 2 and 3 each need a shorter surveillance audit. Estimates only; get at least two quotes from accredited certification bodies.
What Makes Up the Total ISO 27001 Certification Cost?
Five line items make up almost every budget:
- Gap analysis. $3,000 to $8,000. Identifies which controls are missing before you build anything.
- ISMS implementation. $0 if done entirely in-house, $10,000 to $40,000+ if you hire a consultant. This is usually the single largest cost.
- Compliance software (optional). $3,000 to $10,000+ per year. Tools like Vanta, Secureframe, or Scrut automate evidence collection but do not replace the audit.
- Internal audit and penetration testing. $4,000 to $20,000, required before the certification audit.
- External certification audit (Stage 1 and Stage 2). Paid directly to the accredited certification body, usually $7,000 to $25,000 depending on headcount and scope.
The one cost almost no vendor page puts a number on is your own team’s time. Someone, usually a security, IT, or ops lead, will spend weeks pulling together policies, evidence, and documentation. That time has a real cost even when no invoice is attached to it.
Why Do ISO 27001 Certification Cost Estimates Vary So Wildly?
Because three separate things get lumped into one number, and each one scales differently.
- Audit cost scales with headcount, under ISO 27006 rules that certification bodies must follow.
- Implementation cost scales with how mature your existing security processes already are, not your company size.
- Consulting cost scales with how much of the work you want to outsource.
A 20-person company with no documented security policies can end up paying more than a 100-person company that already runs SOC 2 and just needs to map existing controls to ISO 27001. Maturity, not size, is often the bigger driver.
If you are comparing numbers from an older ISO 27001 certification cost 2022 article, treat them as a floor, not a ceiling. Consultant day rates and software subscription costs have both risen since then, and the 2022 edition of the standard, ISO/IEC 27001:2022, is now the only version certification bodies audit against.
What Does ISO 27001 Certification Cost for a Small Business?
For a true small business, under 25 employees with a tightly defined scope, the realistic range is $10,000 to $25,000 for the first year. The cost stays low when:
- The scope covers one product or service, not the whole company
- Existing IT tools (cloud provider, HR system, ticketing) already have decent default security settings
- The team does the gap analysis and documentation in-house using a toolkit instead of a full consultant engagement
Scope is the biggest lever a small business has. Certifying “our SaaS platform and the infrastructure it runs on” costs far less than certifying “the entire company, including every department and office.”
What Does ISO 27001 Certification Cost for a Company With Multiple Locations or Teams?
Once a company has multiple offices, data centers, or business units in scope, audit days increase because the auditor has to assess each location or confirm controls apply consistently across all of them. For a mid-market company (100 to 500 employees) with two or more sites in scope, expect $60,000 to $120,000 in year one, with the audit portion alone often exceeding $20,000.
The practical fix companies use here is scoping: certifying only the business unit or product line that actually needs it, rather than the whole organization, and expanding scope in a later cycle if required.
Is There an ISO 27001 Certification Cost for Individuals?
This is where most searches on this topic go wrong. ISO 27001 certification applies to an organization’s information security management system (ISMS), not to a person. An individual cannot be “ISO 27001 certified” in the same sense a company can.
What an individual can get is training. This is the real answer behind both “iso 27001 certification cost for individuals” and “iso 27001 certification for individuals” searches: people are usually looking for the cost of personal qualifications, not organizational certification.
| Individual qualification | Typical cost |
|---|---|
| Foundation or awareness course | A few hundred dollars |
| ISO 27001 Lead Implementer training | Low thousands, often $1,000 to $2,500 |
| ISO 27001 Lead Auditor training | Low thousands, often $1,000 to $2,500 |
These courses end in a written exam, which is what people usually mean by “iso 27001 certification exam.” Passing it earns a personal qualification certificate from the training provider, not an ISO/IEC 27001 organizational certificate. The two are frequently confused, and no training certificate, however advanced, makes a company or product “ISO 27001 certified.”
What Do the Top-Ranking Guides Say It Costs?
Published estimates for the same certification run from about $4,000 to $200,000, and almost every page quoting them is written by a company selling software or services. Here is what eight of them say, as published and checked in October 2026.
| Publisher | What it sells | Published estimate |
|---|---|---|
| Factorial | HR software | $4,000 to $40,000+ |
| CyberSierra | Compliance software | $6,000 to $40,000+ |
| Drata | Compliance software | $10,000 to $75,000+ over the three-year cycle |
| Copla | Compliance software | €10,000 to €100,000+ |
| Scrut | Compliance software | $15,000 to $60,000 |
| Sprinto | Compliance software | $50,000 to $200,000 |
| GRC Solutions | Consulting and training | £6,250 to £33,750 for the audit alone, by headcount |
| Pivot Point Security | Consulting | $48,000 for one modeled 75-person client |
Three patterns stand out. The low ends cluster between $4,000 and $15,000, which is roughly the audit fee alone for a small company. The high ends swing from $40,000 to $200,000 because each publisher bundles consulting, software, and internal time differently, and the one estimate built on a real client budget lands in the middle.
What Does a Real ISO 27001 Budget Look Like?
Pivot Point Security, a US ISO 27001 consultancy, published a line-item budget for its typical client: a 75-employee SaaS company handling regulated personal data, with partly documented controls and a 12-month deadline.
| Line item | Cost |
|---|---|
| Pre-certification phase 1: scope, risk assessment, gap assessment, remediation plan | $20,000 |
| Pre-certification phase 2: gap closure, ISMS documents, internal audit, audit support | $18,000 |
| Certification audit | $10,000 |
| Total | $48,000 |
Two caveats make this example more useful, not less. The figures reflect 2012 pricing, so treat them as a floor for 2026. The firm also reports that its clients spent anywhere from $5,000 to $70,000 on pre-certification consulting alone, which shows that consulting, not the audit, drives most of the spread.
What Do Companies Actually Report Paying? The Reddit Reality Check
Vendor pages tend to quote wide ranges because the page exists to sell consulting hours or software. Practitioners put it more bluntly: one CISO quoted from a Reddit thread said it costs thousands and takes months, whichever route you take (source: CyberSierra, ISO 27001 cost breakdown).
That matches the real budget above. The audit invoice is the predictable part, while internal time and consulting are where budgets run over. Use your row in the audit-day table plus a realistic consulting figure as your planning number, not the bottom of a vendor range.
Can You Get ISO 27001 Certification for Free?
No, not the certification itself. Three costs cannot be avoided for any organization:
- The accredited certification body’s audit fee
- The time required to build and document an ISMS
- Ongoing surveillance audits to keep the certificate active
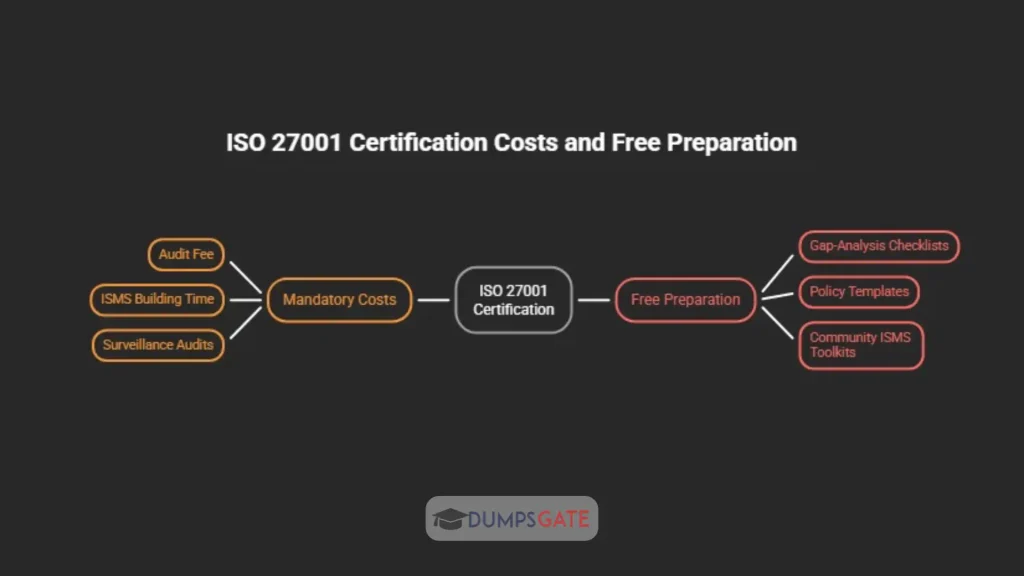
What can be free or near-free is the preparation work. Free gap-analysis checklists, open-source policy templates, and community ISMS toolkits can replace a paid consultant for teams with in-house security knowledge. That can take a $40,000 project down to the cost of the audit alone, often under $15,000 for a small company. “Free” preparation is realistic. A free certificate is not, because an independent, accredited third party has to review and bill for that review.
Why Can a Cheap ISO 27001 Certificate End Up Costing More?
Some low-cost providers issue certificates from certification bodies that are not accredited. If your customer asks for an accredited certificate, that one will not count, and you pay for a second audit.
- ISO does not certify anyone. ISO writes the standard; national accreditation bodies approve the certification bodies that audit you (ISO Help Centre).
- In the US, look for ANAB. US accreditation bodies include ANAB, IAS, and UAF, and ANAB is an IAF signatory, so certificates it accredits are recognized internationally (source: A-LIGN, ANAB accreditation explainer).
- Check before you sign. Look up the certification body, and later your own certificate, in IAF CertSearch, the global database of accredited certificates.
What Are the Ongoing Costs After Certification?
ISO 27001 certification is valid for three years, not indefinitely. Keeping it means a surveillance audit in each of the next two years and a full recertification audit before the certificate expires.
[embed: node/70c5e33a-5dde]
Surveillance audits are shorter than the initial audit, so they cost less. In Pivot Point Security’s example, each surveillance audit ran $7,500, plus $7,000 a year for an outsourced internal audit. Budget for an audit invoice in every year of the cycle, not only the first.
How Can You Lower Your ISO 27001 Certification Cost?
- Start with a gap analysis before hiring a consultant. It tells you exactly what you are paying to fix instead of buying a blanket engagement.
- Keep the scope narrow. Certify the product, team, or system that actually needs it, not the entire company.
- Reuse existing compliance work. SOC 2, ISO 9001, or even a solid security questionnaire response often maps directly onto ISO 27001 controls.
- Compare certification body quotes. Audit fees for the same scope can vary by several thousand dollars between accredited bodies.
- Decide early whether you need a consultant at all. A technically capable internal lead with a toolkit can replace $10,000 to $40,000 of consulting spend.
The Verdict: What Should You Actually Budget?
If you are a small company with a tight, well-defined scope, plan for $15,000 to $25,000 in year one and treat anything under $10,000 as unrealistic unless you already have strong existing documentation. If you are a mid-market or multi-location company, plan for $50,000 to $100,000, and get a scoped quote from at least two certification bodies before committing to a consultant.
Do not let the $200,000 headline figures from enterprise case studies anchor your budget if you are a 30-person team, and do not expect a $5,000 all-in number either. The honest range sits where company size meets how much documentation you already have in place, and the fastest way to bring your real cost down is narrowing scope before you narrow your spending on consultants.
Frequently Asked Questions (FAQs)
How long does ISO 27001 certification take?
Most organizations spend several months preparing, while the certification audit itself takes days, not weeks. Teams with mature controls and a tight scope move fastest (source: GRC Solutions).
Is ISO 27001 certification mandatory?
No. Certification is voluntary: some organizations follow the standard without certifying, while others certify to reassure customers (ISO).
How much does the ISO 27001 standard itself cost?
ISO sells ISO/IEC 27001:2022 for CHF 155, and its 2024 climate-action amendment is free (ISO).
Can a software product be ISO 27001 certified?
No. Certification covers an organization’s ISMS within a defined scope, so a software company can be certified but its product cannot (source: GRC Solutions).
Do individual ISO 27001 qualifications expire?
It depends on the training provider. Some Lead Auditor and Lead Implementer certificates are treated as lifetime credentials, while others require refreshers or continuing professional development (source: SureCloud, individual ISO 27001 certification guide).
How many organizations hold ISO 27001 certificates?
More than 70,000 certificates were reported across 150 countries in the ISO Survey 2022 (ISO).
Sources
- ISO/IEC 27001:2022, ISO
- How to verify an accredited certification, ISO Help Centre
- IAF CertSearch, International Accreditation Forum
- GRC Solutions, “ISO 27001 Cost: What Businesses Need to Know” (updated May 2026)
- Pivot Point Security, “How Much Does ISO 27001 Certification Cost?” (updated March 2025)
- A-LIGN, “Why We Choose ANAB for ISO 27001 and 42001” (April 2025)
- SureCloud, “Can Individuals Get ISO 27001 Certified?” (February 2026)
- CyberSierra, “How Much ISO 27001 Really Costs”
- Published cost pages from Factorial, Drata, Copla, Scrut, and Sprinto, checked October 2026