Quick answer: GRC Analyst Jobs pay a median of roughly $124,910 a year at the closest government-tracked proxy occupation, but entry-level GRC analyst jobs actually start around 55,000-75,000, and many postings labeled “entry level” quietly require 3+ years of experience. GRC Analyst Jobs Remote exist at every career stage, not just junior, and pay varies meaningfully by US state and country. Security+ is the realistic first certification for beginners; CISA and CRISC matter once you have 3-5 years in the field. Read on for the full breakdown, the companies actually hiring, and a 90-day plan to land one.
GRC Analyst Jobs (GRC Analyst Jobs Remote): Pay, Hiring Companies, and Global Salary Data
GRC Analyst Jobs pay a median of roughly $124,910 a year at the information security analyst level, the closest government-tracked proxy occupation, though entry-level GRC analyst jobs typically start much lower, around $55,000 to $75,000, based on live postings reviewed for this guide.[1] There is no federal wage code for “GRC analyst” specifically, and no single country tracks that exact title through an official labor agency. That limitation is stated once here and applies throughout this guide: every number below is either a government-tracked proxy occupation figure or a clearly labeled job-market data point, never an invented one.
Demand for GRC Analyst Jobs Remote has grown alongside the shift toward document- and meeting-based compliance work, which travels well outside an office. What makes this guide different from a standard job-board results page: it covers GRC Analyst Jobs Remote across every experience level, not only entry-level, names the types of companies actually hiring in the US and globally, and breaks out real salary data by US state and by country, not just a single national average.
What Are GRC Analyst Jobs? What Does the Role Actually Do?
A GRC analyst maintains an organization’s risk register, tests security controls against frameworks like SOC 2, ISO 27001, and NIST CSF, collects audit evidence, and tracks third-party vendor risk. The role sits between IT, security, legal, and audit teams. It is less hands-on-keyboard than a security engineer role and more documentation, assessment, and cross-team communication. GRC Analyst Jobs exist across almost every mid-size and large company today because regulators and customers increasingly require documented proof of control effectiveness, not just a policy on paper.
How Much Do GRC Analyst Jobs Pay at Each Level?
| Experience Level | Typical Requirement | Approximate Salary Range (USD) |
| Junior GRC analyst jobs/entry-level GRC analyst jobs | 0-2 years | $55,000-$75,000 |
| Mid-level GRC analyst jobs entry-level candidates grow into | 1-3 years | $75,000-$95,000 |
| Senior GRC analyst | 3-5+ years, certification often required | $95,000-$130,000+ |
| Principal / GRC manager track | 7-10+ years | $130,000-$165,000+ |
| Adjacent benchmark: Information Security Analyst (BLS proxy) | Bachelor’s degree typical | $124,910 median, 29% projected growth 2024-2034 [1] |
GRC Analyst Jobs Remote by Experience Level: What Changes as You Advance?
GRC Analyst Jobs Remote aren’t just an entry-level phenomenon. Reviewing current remote listings across the experience spectrum shows a consistent pattern:
- Junior remote (0-2 years): Focused on evidence collection, vendor questionnaire review, and maintaining the risk register. Certifications rarely required.
- Mid-level remote (1-3 years): Takes ownership of specific GRC workstreams end to end, performs control testing, and begins leading smaller audits. SOC 2 and ISO 27001 familiarity expected.
- Senior remote (3-5+ years): Plans and executes full audit cycles, builds automation for evidence collection, and manages vendor security assessments independently. CISA, CRISC, or CISM frequently required rather than preferred.
- Principal/lead remote (5-10+ years): Owns the GRC platform strategy (tools like AuditBoard or Vanta), negotiates directly with external auditors, and sets control frameworks company-wide.
Which Companies Hire for GRC Analyst Jobs Remote in the USA?
Based on patterns across current remote postings, employers hiring GRC Analyst Jobs Remote in the US cluster into four categories:
- Compliance and security SaaS platforms that build the GRC tooling other companies use: Vanta, Drata, Secureframe, OneTrust, and AuditBoard regularly post remote GRC roles because they also run their own internal compliance programs.
- Audit and assurance firms (MSP/consulting track): Coalfire, A-LIGN, and Schellman perform SOC 2 and ISO 27001 audits for other companies and hire remote GRC analysts and associates at both entry and senior levels.
- Big Four and large advisory firms: Deloitte, PwC, EY, and KPMG run large risk and compliance advisory practices with hybrid and remote-eligible GRC analyst roles, typically client-facing.
- Remote-first technology companies with in-house GRC teams: Cybersecurity and cloud-infrastructure companies such as Rapid7, CrowdStrike, Okta, Cloudflare, and GitLab maintain internal GRC functions supporting their own SOC 2, ISO 27001, and FedRAMP programs, often fully remote by company policy.
Which Companies Hire for GRC Analyst Jobs Remote Globally?
Outside the US, remote GRC hiring concentrates around companies that are remote-first by structure or that run global compliance operations spanning multiple regulatory regimes:
- Fully distributed companies: GitLab, Automattic, and Canonical operate with globally distributed workforces by design and hire GRC and security compliance roles open to candidates across multiple countries.
- Global advisory and IT services firms: Accenture, Wipro, TCS, and Thoughtworks run GRC and IT audit practices across India, the UK, Europe, and Southeast Asia, frequently hybrid or remote within-country.
- India-based Global Capability Centres (GCCs): Multinational banks and tech companies increasingly staff GRC functions out of India-based GCCs, supporting frameworks like SOC 2, ISO 27001, and country-specific rules such as India’s DPDP Act, often at a premium to the standard local market band.
- UK and EU compliance-platform companies: Vendors serving GDPR-heavy markets maintain remote-eligible GRC teams across the UK and EU to support regional regulatory requirements.
GRC Analyst Jobs Remote Salary by US State
No government agency publishes a GRC-specific wage by state. The table below uses the Bureau of Labor Statistics’ state-level wage data for Information Security Analysts, the closest tracked proxy occupation, as a directional benchmark for where GRC Analyst Jobs Remote pay tends to run higher or lower. [1]
| State | Proxy Occupation Median Salary (USD) | vs. National Median |
| Washington | $142,920 | +14% |
| California | $140,660 | +13% |
| New Jersey | $135,390 | +8% |
| New Mexico | $133,780 | +7% |
| Virginia | $132,460 | +6% |
| New York | $131,100 | +5% |
| New Hampshire | $129,690 | +4% |
| Texas | $124,970 | Same as national |
| Maryland | $124,180 | -1% |
| West Virginia | $107,820 | -14% |
A remote GRC Analyst Job listing rarely pays strictly by the candidate’s home state, but employers headquartered in high-cost states like Washington, California, and New Jersey tend to anchor remote pay bands closer to these figures than employers in lower-cost states.
Dig into the details: Is GRC Certification Worth It?
GRC Analyst Jobs Remote Salary by Country
No single international body tracks GRC analyst pay the way the BLS tracks US occupations, so the figures below combine the best available government source (Canada) with consistent, recent job-market compensation data elsewhere. Each is clearly sourced and should be read as a directional range, not an official government statistic outside the US and Canada.
| Country | Approximate Annual Salary Range | Source Type |
| United States | 55,000-130,000+ (USD), $124,910 proxy median [1] | Official (BLS) |
| Canada | Approximately $103,000 CAD median for cybersecurity specialists (NOC 21220), converted from a $49.52/hour median wages [2] | Official (Government of Canada Job Bank) |
| United Kingdom | Roughly £50,000-£65,000 | Job-market benchmarking (IT Jobs Watch) |
| Germany | Roughly €55,000-€75,000 | Job-market benchmarking (Glassdoor Germany) |
| Australia | Roughly AU98,000-AU123,000 | Job-market benchmarking (SEEK/Payscale via industry career guides) |
| India | Roughly ₹5 lakh-₹14 lakh (6,000-17,000 USD equivalent) for GRC-titled roles, with Global Capability Center roles often paying 25-40% above this band | Job-market benchmarking (industry career guide) |
Entry-level GRC analyst remote pay is lowest relative to the cost of living in markets with large GCC and offshore delivery hubs, while cybersecurity GRC analyst jobs in the US, Canada, and Australia command the highest absolute pay globally, based on the sources above.
Delve into the details of: Everything You Need To Know About CGRC Certification
Are Entry Level GRC Analyst Jobs Really Entry Level?
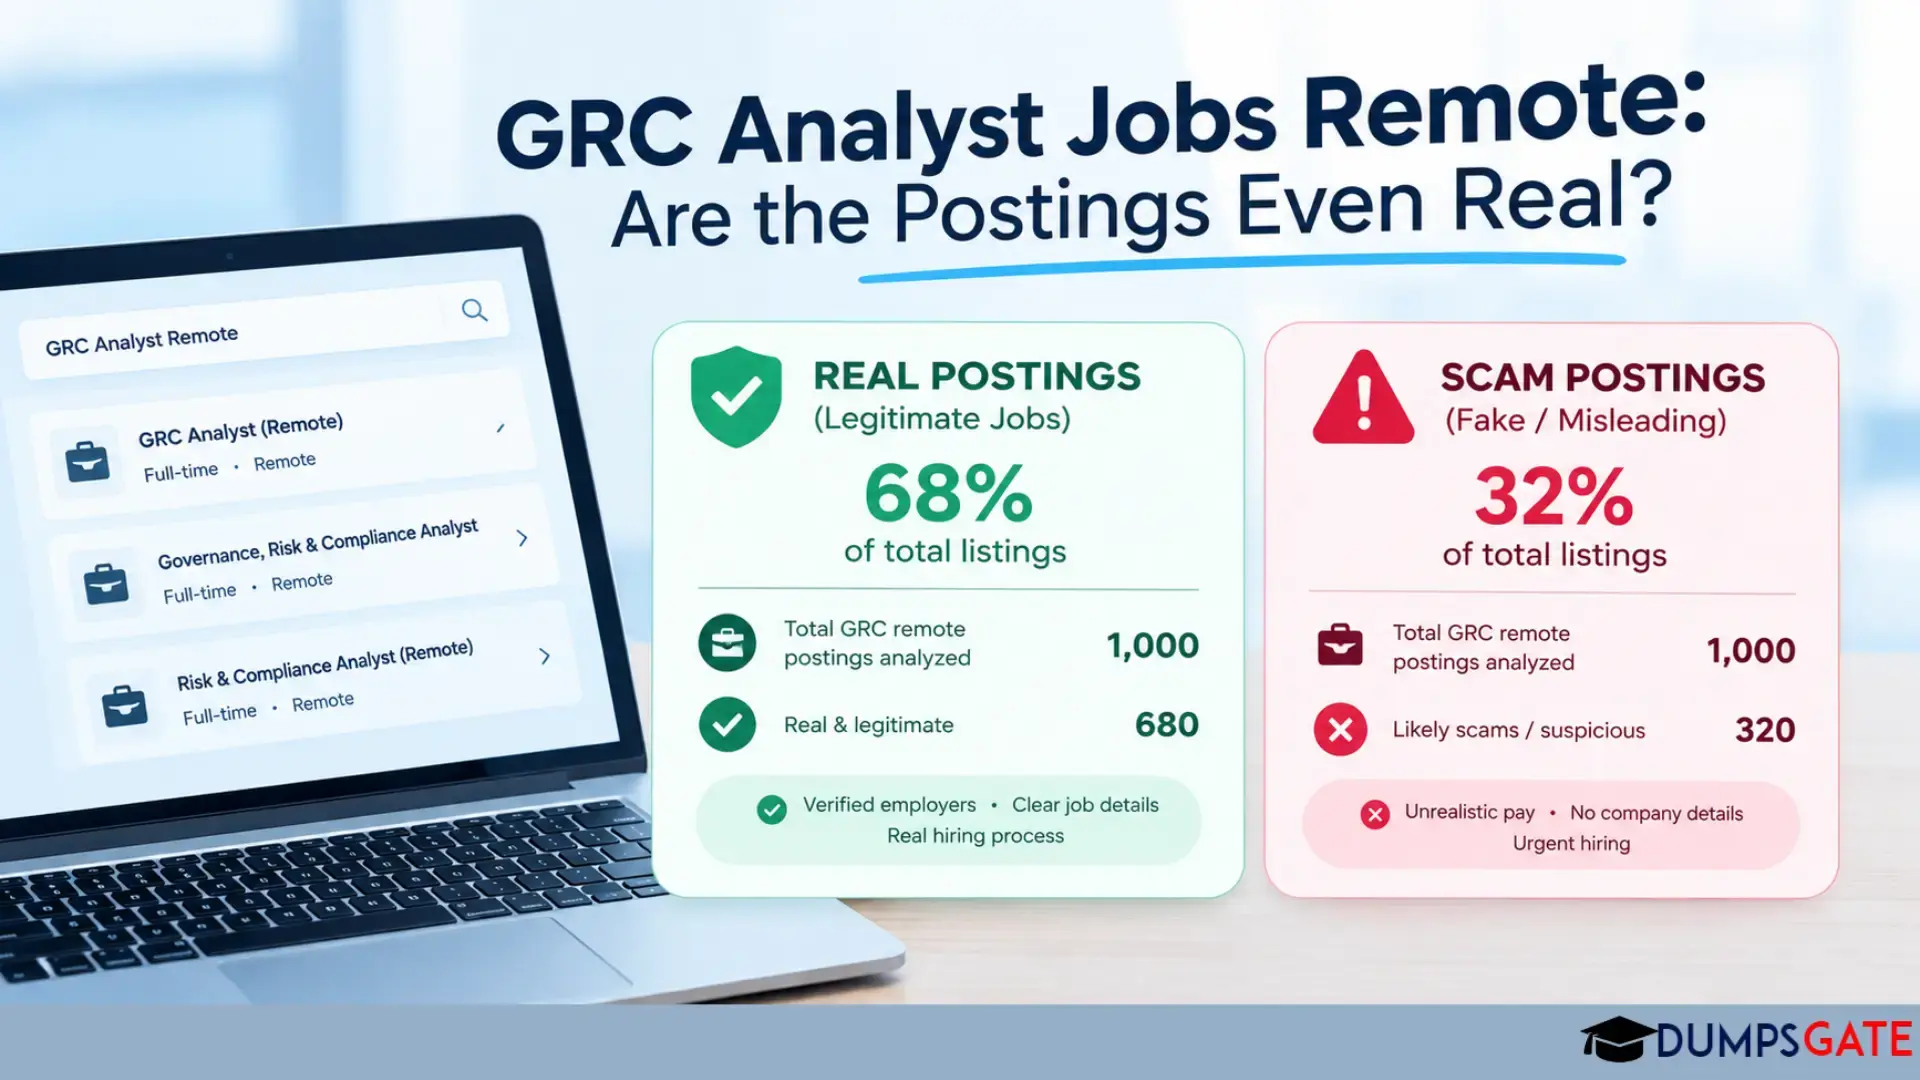
Partially, and this is the most common frustration job seekers report in this space. Reviewing current postings shows a clear split:
- Genuinely entry-level: 0-2 years required, bachelor’s degree in a related field, certifications listed as “preferred” not mandatory, emphasis on “willingness to learn.”
- Mislabeled entry level: Title says “entry level” or “junior,” but the requirements section asks for 3-5 years in GRC, risk, or audit. This functions as a soft filter, not a true beginner opening.
When evaluating remote entry-level GRC analyst jobs, read the required-experience line first. Titles are inconsistent across employers; the years-of-experience field is not.
Learn more about: Unveiling The 10 Best GRC Certifications in 2026 To Elevate Your Career
What Do Junior GRC Analyst Jobs Typically Require?
Across postings reviewed for this guide, the recurring requirement pattern for junior GRC analyst jobs includes:
- A bachelor’s degree in cybersecurity, information systems, business, or a related field, or equivalent experience
- 0-2 years of experience in GRC, compliance, risk, or audit
- Familiarity with at least one framework: SOC 2, ISO 27001, NIST CSF, or HIPAA
- Proficiency with Microsoft Office or Google Workspace
- Strong written communication, since GRC work is documentation-heavy
Certifications are frequently listed as “preferred,” not required, at the junior level. That is a meaningful difference from mid- and senior-level cybersecurity GRC analyst jobs, where CISA, CRISC, or CISM are often mandatory rather than optional.
Explore further: CISA vs CIA Certification: Which One Is Better In 2026?
What Certifications Actually Help With Cybersecurity GRC Analyst Jobs?
| Certification | Issuing Body | Exam Fee (2026) | Typical Prep Time | Best Fit |
| CompTIA Security+ | CompTIA | $425 list price for a standard voucher [3] | 6-10 weeks | Best entry point for junior grc analyst jobs remote with no prior security background |
| CISA (Certified Information Systems Auditor) | ISACA | $575 for members, $760 for non-members, plus a $50 one-time application fee | 10-16 weeks | Mid-to-senior IT audit and GRC roles; full certification requires 5 years of relevant experience |
| CRISC (Certified in Risk and Information Systems Control) | ISACA | Comparable fee structure to CISA; verify current pricing directly with ISACA | 8-12 weeks | Risk-focused GRC roles |
You can sit the CISA exam before meeting the experience requirement, but ISACA will not issue the credential until you submit verified experience within five years of passing. That makes Security+ the more realistic first step for someone pursuing entry-level GRC analyst jobs remote without a security work history.
Learn more about: CompTIA Security+ SY0-801 vs SY0-701: What’s Changing in 2027
How Do You Land GRC Analyst Jobs Remote With No Experience?
- Earn one framework-aligned credential first. Security+ is the lowest-cost, fastest entry point.
- Build a visible project: document a mock SOC 2 control matrix or risk register for a fictional company and publish it on GitHub or LinkedIn.
- Target junior GRC analyst jobs and GRC-adjacent roles, such as compliance coordinator, IT auditor associate, or security analyst I, as lateral entry points, not only roles with “GRC” explicitly in the title.
- Filter applications by the actual stated experience requirement, 0-2 years, not by the word “entry level” in the title.
- Prioritize MSP and consulting-track employers, which hire at the 0-3 year range more frequently than in-house SaaS compliance teams in postings reviewed for this guide.
GRC Analyst Jobs Near Me vs. GRC Analyst Jobs Remote: Which Should You Target?
Remote GRC work is increasingly viable because it’s document- and meeting-based rather than hands-on hardware work. In 2025, 34.9% of full-time workers, about 32.5 million people, worked from home at least part of the day on average, up from 33.4% in 2024.Remote can materially increase the available pool, since SaaS and MSP companies frequently hire nationally rather than restrict by metro area.
What Should Your First 90 Days of Searching for GRC Analyst Jobs Look Like?
- Weeks 1-3: Finish one certification, Security+ recommended, and build your control-matrix sample project.
- Weeks 4-6: Apply to 5-8 entry-level GRC analyst jobs per week, prioritizing postings that state 0-2 years required rather than ones that only say “entry level” in the title.
- Weeks 7-10: Network directly with GRC managers at target companies. GRC teams are small, so referrals carry more weight than in larger engineering orgs.
- Weeks 11-13: Expand your search to adjacent titles, compliance analyst, IT audit associate, security operations analyst, if direct GRC titles are not converting to interviews.
Read more: GRC Analyst From Zero: What Actually Gets You Hired in 2026?
Verdict: Are GRC Analyst Jobs Worth Pursuing Right Now?
Yes, with a realistic entry strategy and a clear view of where the pay actually sits. The adjacent information security field is projected to grow 29% through 2034, far faster than the average occupation, signaling durable demand for risk and compliance skill sets even though GRC-specific wage data is not separately tracked anywhere.<sup>[1]</sup> Candidates without experience should treat Security+ as the entry credential, target postings with a true 0-2-year requirement rather than misleadingly labeled “entry level” roles, and use GRC Analyst Jobs Remote search, including companies outside their home country when visa and tax status allow, to offset a thin local market. CISA and CRISC remain the credentials that unlock mid-to-senior cybersecurity GRC analyst jobs, and pay scales vary meaningfully by both US state and country, so a remote search strategy should account for both the role level and the employer’s home-market pay band.
Frequently Asked Questions About GRC Analyst Jobs
What does a GRC analyst do?
A GRC analyst tests security controls, maintains risk registers, collects audit evidence, and manages third-party vendor risk assessments across frameworks like SOC 2 and ISO 27001.
Is GRC a good entry-level job?
It can be, when the posting genuinely requires 0-2 years of experience. Many postings labeled “entry level” actually require prior GRC, risk, or audit experience, so check the stated requirement, not the title.
What certifications do I need to be a GRC analyst?
None are strictly required at the junior level. CompTIA Security+ is the most accessible starting credential; CISA and CRISC become relevant for mid-to-senior cybersecurity grc analyst jobs.
How do I become a GRC analyst with no experience?
Earn Security+, build a visible sample project such as a mock control matrix, and apply to postings that explicitly state 0-2 years required, including adjacent titles like compliance coordinator.
What is the difference between GRC and cybersecurity?
Cybersecurity roles build and defend technical systems. GRC roles govern, assess, and document whether those systems meet risk, compliance, and audit requirements.
How much does a GRC analyst make?
Entry level grc analyst jobs typically pay $55,000 to $75,000 in the US. Senior GRC roles with a certification can reach $95,000 to $130,000 or more domestically, with meaningfully different bands outside the US as shown in the country table above.
Which companies hire the most for GRC Analyst Jobs Remote?
Compliance SaaS platforms (Vanta, Drata, OneTrust), audit firms (Coalfire, A-LIGN, Schellman), Big Four advisory practices, and remote-first technology companies with their own internal GRC programs are the most consistent sources of remote postings reviewed for this guide.
Does GRC analyst pay vary a lot by US state or by country?
Yes. The proxy-occupation data above shows roughly a 30% spread between the highest-paying state (Washington) and the lowest (West Virginia), and an even wider spread internationally, with India’s typical band running well below the US, UK, Canada, and Australia bands.